Scope3 CSRD: Why Procurement Must Lead Supplier ESG Data Collection
Scope3 CSRD: How to Industrialise Supplier ESG Data in Source-to-Pay Scope3 CSRD forces organisations to collect ESG and emissions data outside their perimeter—across hundreds or thousands of suppliers—while meeting audit-ready traceability expectations. Procurement is best placed to industrialise collection through onboarding, contracts, and recurring supplier governance, improving data quality over time without creating supplier fatigue. […]
Supplier Documents: How AI Accelerates Analysis Without Losing Compliance Control
Supplier Documents: AI Verification With Human Oversight & Audit Trails Supplier documents create a compliance bottleneck at scale: certificates, licences, attestations, ESG declarations, and contract appendices must be checked, renewed, and provably controlled. AI can accelerate verification, but the safe path is “human-in-the-loop” governance—automated checks for standard cases, clear escalation for exceptions, and an audit […]
Supplier Risk: How Procurement & Risk Teams Collaborate at Scale
Supplier Risk: Shared Governance, Workflows & KPIs for Joint Control Supplier risk is now a cross-functional enterprise issue: one supplier failure (financial, cyber, regulatory, operational) can cascade in hours. The most resilient organisations align procurement and risk teams on a shared risk appetite, joint governance, and automated workflows—so decisions stay fast and defensible. In Europe’s […]
Supplier risk: how IT leaders drive organisation-wide risk reduction
Supplier risk: why it’s now a CIO-level resilience priority Supplier risk : the SolarWinds breach proved that enterprise security depends on third parties. For CIOs, reducing supplier risk is no longer a procurement checklist—it’s core to resilience, cybersecurity governance and regulatory compliance, at scale. For CIOs and IT leaders, supplier risk management is no longer […]
TPRM Europe : leading platforms for supplier & third-party risk
TPRM Europe : why supplier risk governance is structurally different TPRM Europe : European organisations need automated, evidence-driven third-party governance as supplier incidents (cyber, regulatory, financial, ESG) cascade faster than annual audits can detect. The shift is from periodic checks to continuous, integrated oversight across ERP, GRC and procurement workflows. European supplier risk management has […]
TPRM integrations : best ERP & GRC integrations for third-party risk
TPRM integrations : breaking down ERP & GRC data silos TPRM-integrations : when third-party risk, procurement, and compliance data sit in disconnected ERP and GRC systems, organisations lose real-time visibility and create audit exposure. The goal is a unified, measurable control layer where vendor risk signals flow into procurement decisions and governance becomes traceable. Organisations […]
Assessing Cyber Risk in Your Suppliers: Why & How to Transform Your Practices
The growing dependence of companies on vast, interconnected digital ecosystems is radically reshaping how cyber risk must be approached. The 2025 edition of the TPRM Observatory, conducted by Board of Cyber and CESIN, confirms a now-central trend: cyber risk from suppliers is no longer peripheral — it has become strategic, and is now recognized as […]
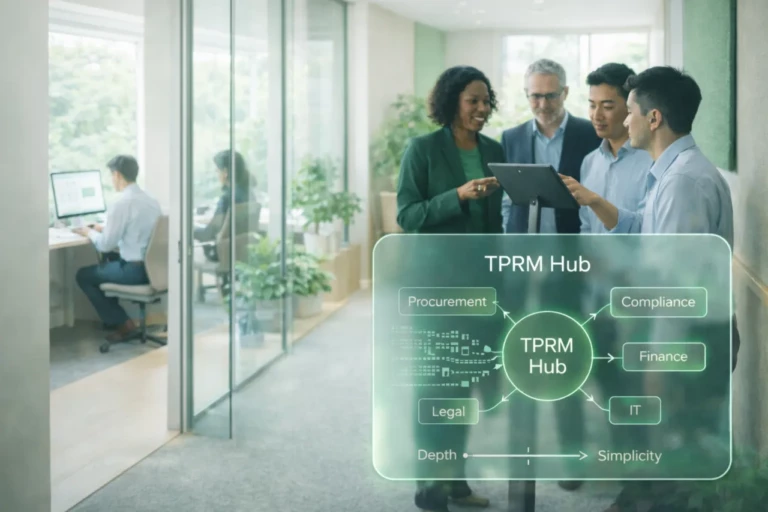
TPRM silos: how to break down barriers
Quick answer: TPRM silos fragment third-party governance across Procurement, Legal, Compliance, Finance, and IT, which increases duplicate work and slows risk decisions. A TPRM platform can centralise supplier data into a single system of record and help teams run collaborative assessments. In large deployments, this approach has been associated with 25% administrative time saved (about […]
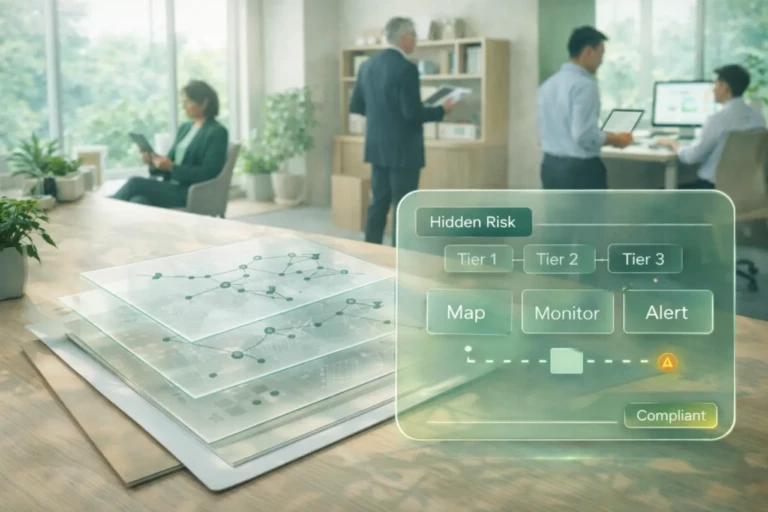
Hidden Supplier Risks: Why Procurement Leaders Still Underestimate Them
Hidden supplier risks often sit in tier-2/3 networks. Learn the real cost of blind spots and how continuous monitoring reduces disruption exposure.